
Seven years of past tax returns, digitized real estate deeds, wills, and brokerage export logs contain your complete financial identity. Storing these records on standard thumb drives or unencrypted external hard disks exposes you to identity theft if a drive is misplaced. Using hardware-encrypted USB drives for financial records isolates your personal balance sheet from host-level digital threats.
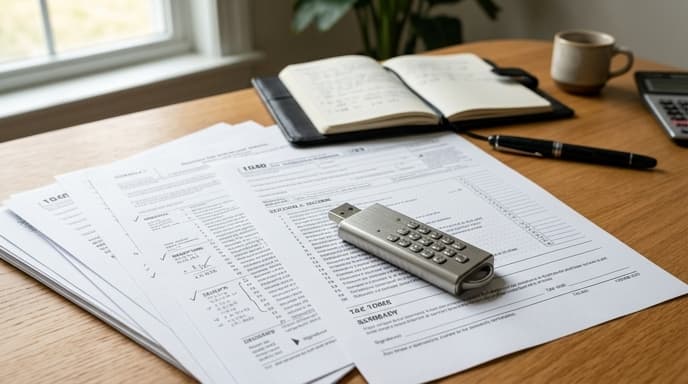
Unlike software containers that rely on operating system memory, hardware-encrypted storage handles decryption on an onboard microchip. The underlying controller architecture ensures documents remain unreadable to unauthorized finders.
On-Board Cryptographic Processors vs Software Encryption
Standard USB drives require host software like BitLocker or VeraCrypt to encrypt data blocks. While functional, software encryption exposes your cryptographic master keys to the computer's RAM, leaving them accessible to memory scrapers and keyloggers on an infected host.
Dedicated hardware-encrypted flash drives use an isolated cryptographic microprocessor. The encryption key is generated, stored, and executed inside the drive's casing. The host computer never handles the key; it sees an unmounted, inaccessible storage partition until hardware authentication succeeds.
Physical PIN Keypads vs Software Unlock Prompts
The authentication interface dictates how the drive handles security:
- On-device alphanumeric keypads: Drives with mechanical buttons or touch pads allow you to enter your PIN before plugging the device into a USB port. This prevents host keyloggers from capturing your passcode.
- Capacitive touch wear resistance: Drives with polymer-coated buttons resist surface wear, preventing printed keypad digits from revealing your passcode over time.
- Software pop-up unlockers: Encrypted drives that require running a host executable fail on systems where you lack administrative install privileges or on mobile operating systems.
Physical Tamper Proofing and Brute-Force Self-Destruct
If physical possession of your financial records is compromised, hardware security ratings determine resistance against extraction. Look for drives certified under standards like FIPS 140-2 Level 3 or FIPS 140-3.
These standards require internal memory chips and controller circuits to be potted in an opaque epoxy resin. Attempting to slice open the casing to probe flash NAND chips strips the electrical traces and destroys the data. Furthermore, robust hardware tokens permanently wipe internal cryptographic keys after a set number of consecutive incorrect PIN attempts (typically ten), rendering the data unrecoverable.
Frequently Asked Questions
What happens if I forget the PIN to my hardware-encrypted drive?
Because there is no external backdoor or master reset mechanism, forgetting your PIN results in permanent data loss once the brute-force threshold is hit. Maintain an independent physical copy of your PIN in a secure location.
Can hardware-encrypted drives be infected by computer viruses?
An unlocked drive can store an infected file just like standard media, but many hardware drives feature an onboard physical or software-enforced read-only switch. Enabling read-only mode prevents malware from writing to the storage when opening files on unfamiliar computers.
Does hardware encryption slow down read and write transfer speeds?
Modern crypto-controllers run at line rate. They process XTS-AES 256-bit encryption without creating noticeable data bottlenecks across standard USB 3.0 or USB 3.2 interfaces.
Key Takeaways
- Hardware-encrypted storage shields financial records by managing keys off the host computer's RAM.
- Physical alphanumeric keypads prevent software keyloggers from capturing your unlock PIN.
- FIPS certification indicates internal epoxy potting that destroys memory chips if physical tampering occurs.
- Brute-force protection erases internal master keys after repeated failed PIN attempts.
- Keep a separate, secure paper record of your recovery PIN to avoid permanent lockouts.
Related Reading
- Hardware Security Keys: Comparing FIDO2, NFC, and USB-C Specs for Banking
- Workstation Compartmentalization: Running Financial Accounts in Isolated Virtual Machines
- Configuring Browser Profile Isolation Exclusively for Online Banking