
While multi-factor authentication reduces account takeover risks, relying on consumer smartphones for one-time passcodes introduces other vulnerabilities. Mobile malware, operating system lockouts, SIM swaps, and dead batteries can lock you out of banking portals. Using hardware TOTP tokens for banking isolates your authentication credentials on an air-gapped device.
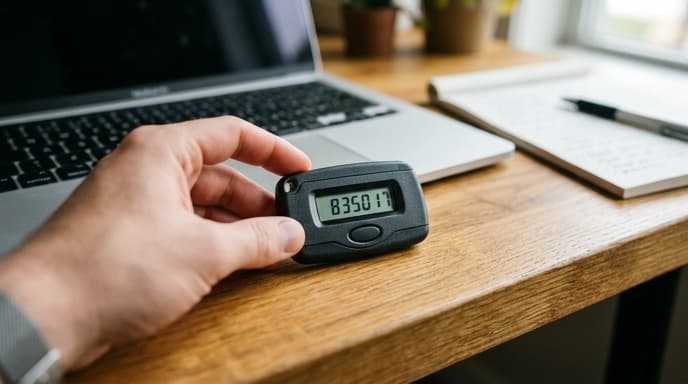
These dedicated security devices generate the same six-digit codes as mobile authenticator apps, but work completely offline without an internet connection, cellular radio, or general-purpose operating system.
The Core Architecture: RFC 6238 and Isolated Clocks
Time-based One-Time Passwords (TOTP) rely on the open IETF RFC 6238 cryptographic standard. The system combines a shared secret key (provided during setup) with the current timestamp, hashing them to generate a changing six-digit passcode every thirty seconds.
In a hardware token, this calculation occurs inside an isolated silicon microchip powered by an internal battery. The token uses a real-time quartz crystal clock oscillator. Because the device has no Wi-Fi, Bluetooth, or cellular antennas, an attacker cannot extract the cryptographic seed remotely without physical access to the token.
Factory-Programmed vs Field-Programmable NFC Tokens
When choosing standalone authentication tokens, the way the shared secret seed is loaded into the device is the main architectural difference:
- Factory-locked tokens: Ship with a pre-burned secret seed generated by the manufacturer. The vendor provides an encrypted configuration file containing the seed, which must be imported into enterprise identity management systems. These do not work for consumer banking because financial institutions require you to scan their specific QR code.
- Programmable NFC tokens: Work with retail banking accounts. These tokens include an NFC receiver. You use an open-source tool on a smartphone once during setup to write your bank's QR code secret into the card. After configuration, the token generates passcodes independently, and the NFC interface can be permanently locked with a master password.
Time Drift and Battery Longevity Specifications
Because hardware tokens lack internet access to synchronize with network time servers, their internal quartz clocks experience minor timing variances known as "time drift." Over several years, an uncalibrated quartz oscillator can drift ahead or fall behind network time by several seconds.
High-grade tokens use temperature-compensated crystal oscillators that keep time drift to less than a few seconds per year. Financial institutions typically configure an acceptance window that tolerates time variance of one step (thirty seconds in either direction), but severe drift eventually causes valid codes to be rejected. In addition, check the battery: quality tokens use low-power e-ink or liquid crystal displays (LCD) paired with industrial lithium cells, providing an operating life of five to seven years before replacement is required.
Frequently Asked Questions
How does a hardware TOTP token differ from a FIDO2 security key?
FIDO2 keys use public-key cryptography to perform an interactive, phishing-proof handshake directly through USB or NFC. Hardware TOTP tokens display a visual six-digit number on a screen, which you type into the banking website manually.
What happens when the hardware token's internal battery dies?
Because these devices are sealed to prevent physical tampering, the internal battery cannot be replaced. When the battery depletes, the device stops working, and you must link a replacement token using your bank's account recovery process.
Can I register the same bank QR code to two different hardware tokens?
Yes. If you display your bank's setup QR code on your screen, you can scan and program that same secret seed into two separate programmable hardware tokens, creating an offline physical backup.
Key Takeaways
- Hardware TOTP tokens generate two-factor codes in an air-gapped environment without cellular or Wi-Fi connectivity.
- Programmable NFC tokens allow you to store consumer banking QR code seeds directly on standalone hardware.
- Internal quartz clocks experience minor time drift; look for temperature-compensated timing specifications.
- Tokens feature sealed industrial lithium batteries that provide five to seven years of continuous operation.
- Dedicated hardware tokens are immune to mobile malware and smartphone operating system lockouts.
Related Reading
- Push Notifications vs Hardware TOTP Tokens for Banking Authorization
- Hardware Security Keys: Comparing FIDO2, NFC, and USB-C Specs for Banking
- Configuring YubiKey FIDO2 Security on Retail Brokerage Accounts